Cybersecurity
Configuring Technology Insurance Company Infrastructure
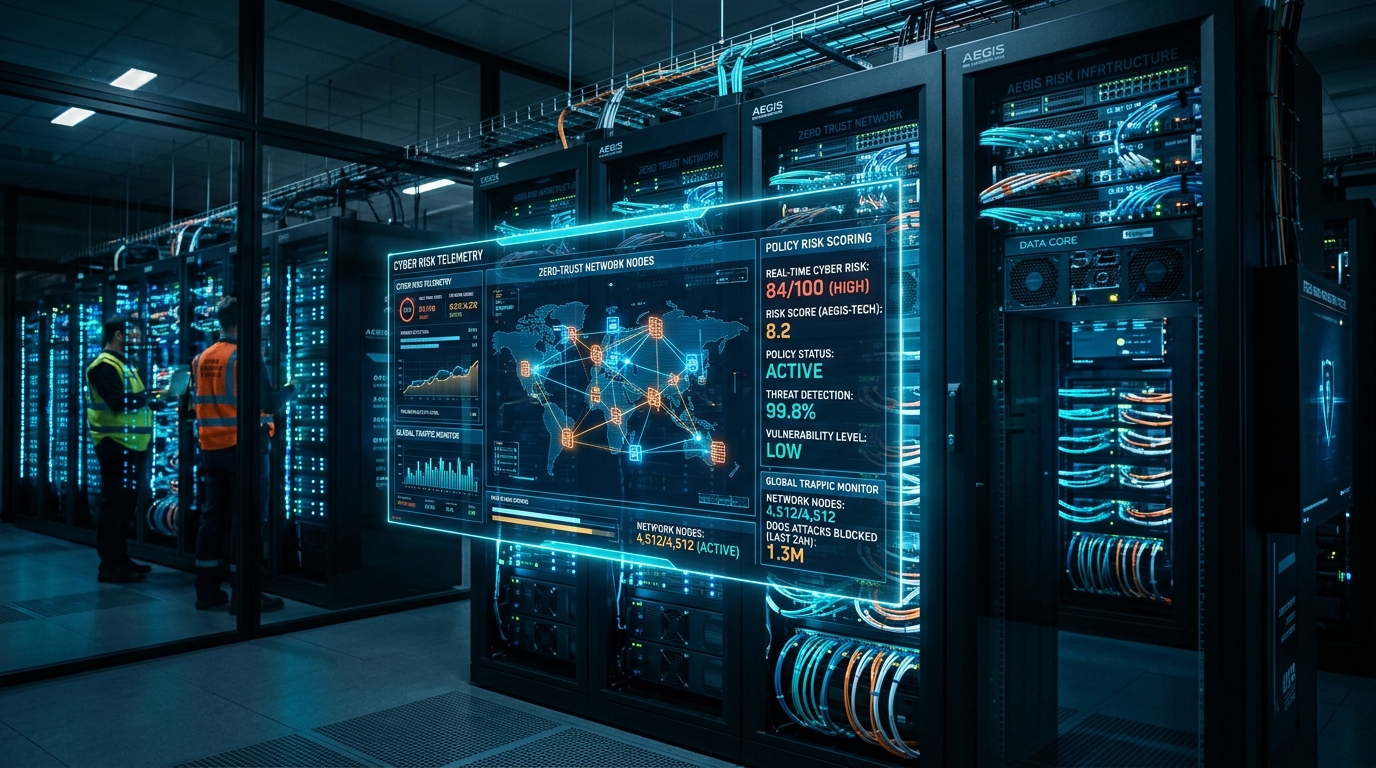
A technology insurance company secures cloud infrastructure, scales throughput, and optimizes actuarial risk calculation models.
Cora Lee2026-09-25
Actionable security reports on zero trust architecture, threat intelligence, vulnerability research, and modern defensive tooling.
A technology insurance company secures cloud infrastructure, scales throughput, and optimizes actuarial risk calculation models.

What guidance identifies federal information security controls, outlining NIST SP 800-53, FIPS 200, and compliance frameworks.

Deploying cyber security solutions across distributed infrastructure demands zero-trust architecture, endpoint isolation, and automated incident response.
Understanding what is malware requires dissecting polymorphic payloads, memory injection techniques, and zero-day defense mechanisms across enterprise IT.
An information technology specialist engineers scalable network infrastructure, enforces enterprise cybersecurity, and automates server deployments today.
Cybersecurity analysis at Com Pors investigates defensive system design, threat intelligence protocols, and cryptographic resilience. We evaluate zero-trust network architectures, TLS 1.3 implementation details, memory-safe programming paradigms, and endpoint isolation mechanisms. Our research provides systems administrators and security engineers with pragmatic guidance on threat mitigation, runtime application protection, and rapid incident recovery.
Our technical analysts scrutinize operating system security boundaries, container breakout prevention, and eBPF-based runtime monitoring. Rather than treating security as an isolated perimeter appliance, our reports demonstrate how to enforce defensive boundaries across every layer of the compute stack. We examine mutual TLS handshakes, hardware-backed security modules, automated certificate renewal lifecycles, and kernel privilege separation.
In the realm of enterprise resilience, Com Pors investigates incident response orchestration and cryptographic agility. We assess post-quantum lattice-based encryption standards, immutable backup architectures, automated vulnerability scanning pipelines, and zero-day patch rollouts. Every guide is designed to help organizations build verifiable defense-in-depth mechanisms against persistent adversaries.
Moreover, our security reporting covers identity federation protocols (SAML 2.0, OIDC, WebAuthn) and hardware security key enforcement. We investigate privilege escalation attack vectors, supply chain code auditing protocols, and automated software bill of materials (SBOM) validation to eliminate backdoor risks in enterprise environments.
Our team tests systems on physical lab servers. We record memory limits, CPU cycles, and network speeds. We do not use vendor marketing claims or press releases.
Every guide accounts for CPU caches and network ports. We focus on memory layout and fast non-blocking sockets. This keeps software fast, clean, and stable under load.
Our benchmarks use eBPF probes and hardware counters. We record delay spikes under load. This helps engineers spot system slowdowns on live servers.
We test system behavior during network drops and hardware faults. Our guides show how to tune circuit breakers. We show how to keep databases online during cloud outages.
We share our test scripts in public code repos. Any engineering team can clone our repos. You can verify the exact test numbers on your own hardware.
All reports undergo strict review before publication. Senior system architects verify our findings. We do not accept sponsored ads or paid vendor reviews.
Our technical research lab runs continuous evaluations across cloud infrastructure, enterprise security networks, and server hardware. We measure raw throughput, memory latency, and packet loss under peak stress. All test results are documented with open-source scripts so engineering teams can reproduce our findings.
We review system architectures against established industry standards. Each report focuses on practical reliability, zero-trust security boundaries, and predictable resource allocation. We exclude marketing claims and focus strictly on empirical benchmarks.